Managed Security Operations
Strengthen monitoring, detection, triage, and response workflows with practical support for your security operations.
Learn More →
CYBLU helps organizations operationalize security through monitoring, detection engineering, incident triage, threat hunting, and response guidance.
Get Your Cyber Exposure AssessmentStrengthen monitoring, detection, triage, and response workflows with practical support for your security operations.
Learn More →Identify weaknesses, prioritize exposure in business context, and guide remediation beyond the scan report.
Learn More →Connect external assets, credential exposure, and digital risk signals to a prioritized plan for reducing risk.
Learn More →We support security monitoring, threat investigation, and response planning to help your team make informed decisions and reduce operational risk.
Efficient cybersecurity strategy must be proactive and customized. Our specialists design and develop an incident response program tailored to your business, with strategy, organization, technology, and procedures, as well as a comprehensive assessment of your attack surface
Review relevant event data and logs from the agreed systems, networks, and endpoints. Monitoring scope, coverage, and escalation responsibilities are defined with your team.
Develop and tune detection use cases, review alerts, and prioritize investigations. Focus security operations on relevant signals and actionable response.
Activate our incident response capabilities to ensure malicious actors are blocked and contained quickly with in-depth attack triage. Let the Cyblu team find out the root cause of the activity and create tailored processes to fill your security gaps. It’s also crucial to reduce your operational downtime during remediation
Reverse engineering on the malware samples to uncover hidden IOCs
Assess the effectiveness of security operations with conversational incident simulations
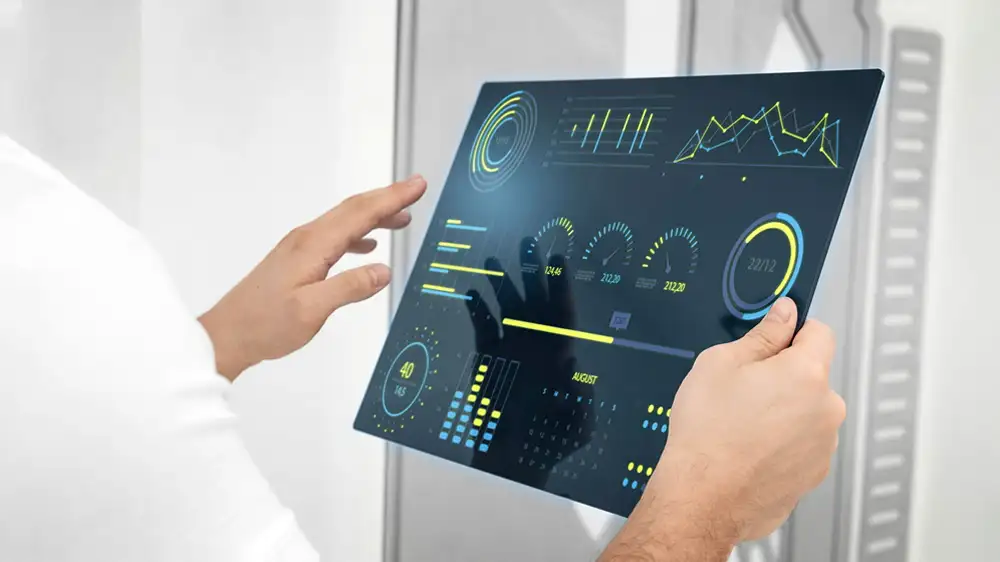
Customizable dashboards to monitor alerts incident response metrics and patterns
Evidence based knowledge and actionable recommendations for evolving cyber threats
Understand the root-cause and scope of the security incident
Leverages a hypothesis-based approach to catch active threats and vulnerabilities
◷ June 01, 2023
◷ July 15, 2023
◷ July 15, 2023